unsupported_builtinThe policy uses a Rego built-in with no equivalent in the target provider's control model.
PLATFORM / MULTI-CLOUD
Every cloud has its own guardrail format, and a policy written three times drifts three ways. GovernorAI compiles one governance policy into the native control configuration of each supported provider — and where a policy cannot be expressed in a target, it says so and refuses rather than emitting something weaker.
THE CONNECTION
Write the rule once and govern the agents in your own data centre, in all three clouds, in Databricks, in the SaaS platforms your business runs on, and in whatever framework your teams build with. And the way GovernorAI is meant to be connected, it never receives a credential that could create a role in your account — it generates the template, your operator runs it.
Kubernetes manifests, Helm chart, RBAC and network policy. The agents never leave your network.
A CloudFormation stack and a console link. Teardown refuses to remove anything it cannot prove GovernorAI created.
One policy, rendered into each provider’s own native control format. The guided install is furthest along on AWS today.
An egress agent on every node, pinned by a cluster policy — a cluster created against it cannot omit governance.
Salesforce and ServiceNow run a package in your org that can abort the write. Workday connects as the HR source that decides who approves.
MCP, the SDKs, and an Envoy filter — governed at the enforcement point the call already crosses.
Per-run credentials scoped by an inline session policy are implemented in the AWS connector but off by default. Stated that way rather than as a shipped default, because a capability behind a flag is not a capability you have.
THE COMPILER
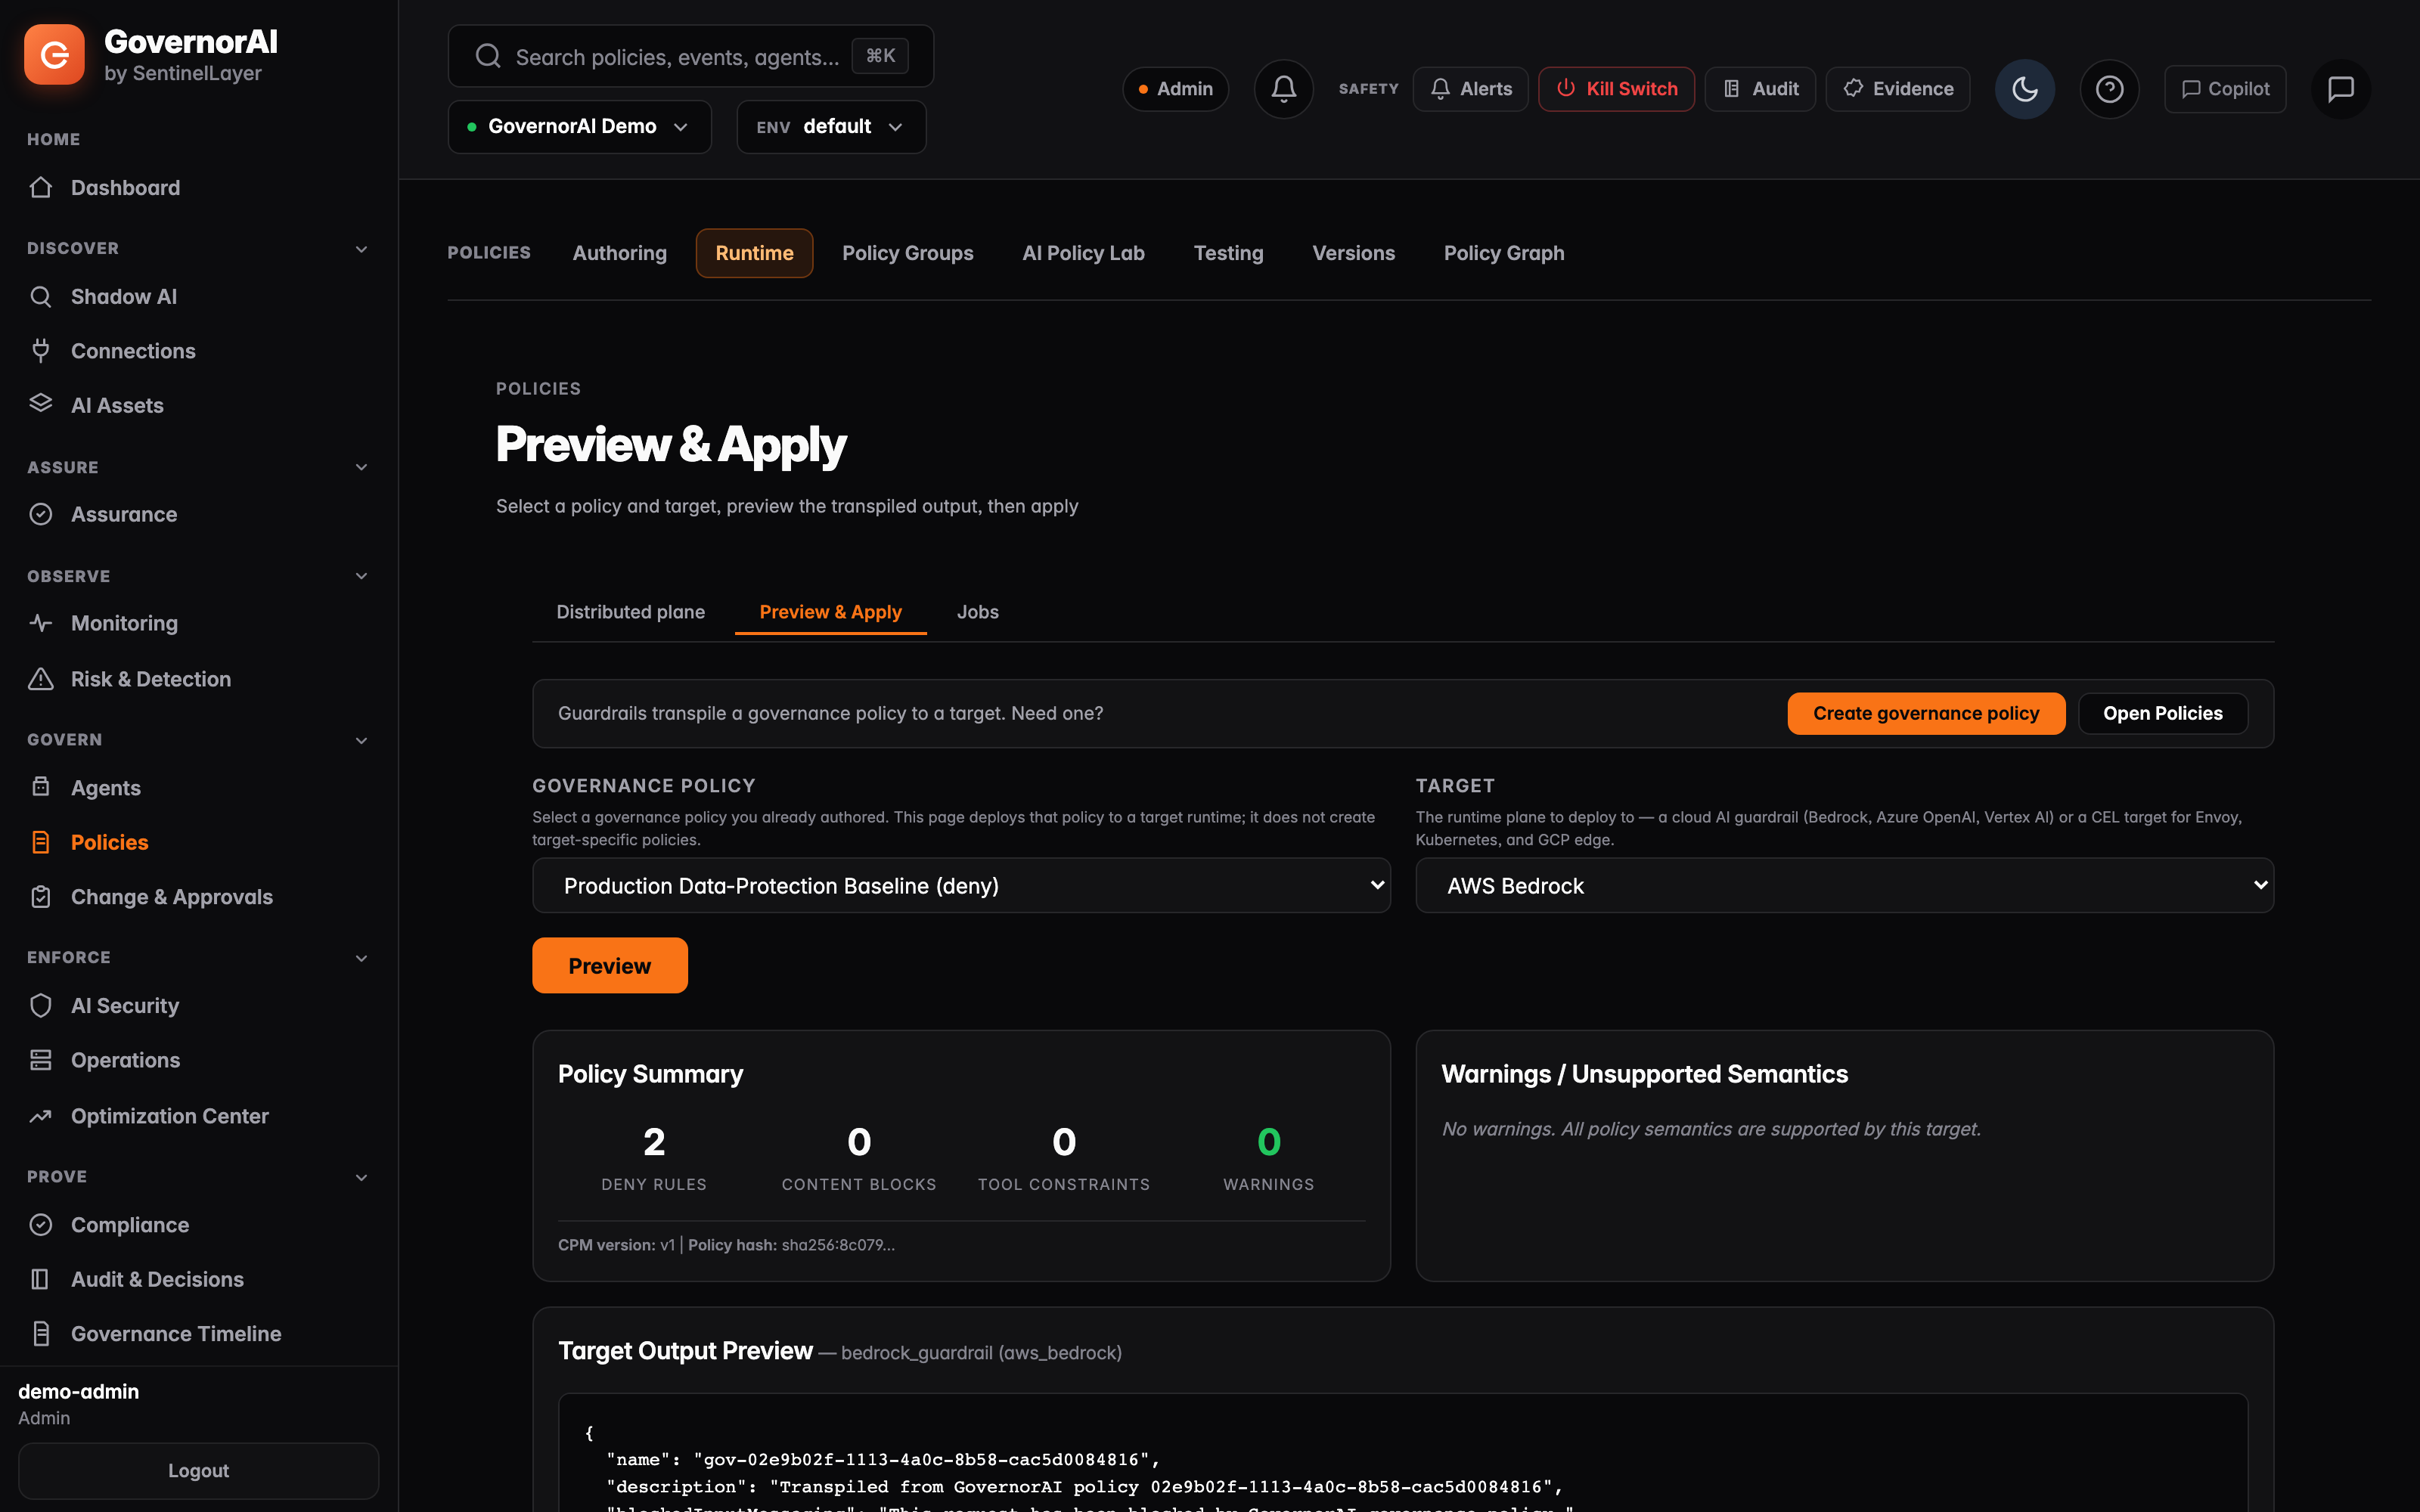
Compilation, not translation at runtime. The policy is parsed statically — using OPA's AST parser rather than its evaluation engine — into an intermediate Common Policy Model, and each provider adapter renders that model into that provider’s own control format. What you get back is the artefact — yours to review, diff and apply. GovernorAI does not push configuration into your account on its own authority, which is the same boundary the connection above is built on.
The policy your platform team already reviews, in the language they already use.
OPA's AST parser reads the policy statically and produces a provider-neutral model. Nothing is evaluated to build it.
Each target renders the model into its own control format, or reports that it cannot.
aws_bedrockazure_openaigcp_vertexTwo U.S. provisional applications are on file.
DIVERGENCE IS PRINTED
This is the part that makes the rest usable. A compiler that silently drops what it cannot express produces a config that looks complete and enforces less than the policy said — the worst possible outcome for a governance artefact. Three reasons are produced today; the error contract reserves a fourth that no validator currently emits.
unsupported_builtinThe policy uses a Rego built-in with no equivalent in the target provider's control model.
external_dataThe policy consults data the provider control cannot reach at decision time.
non_deterministicReserved, not yet emitted. The contract defines it for a policy that would not resolve the same way twice; no validator produces it today.
wrong_packageThe policy is not in the governance package the compiler reads.
Where a source location applies, the error identifies it — an unsupported built-in or an external-data lookup points at the line to change. A package-level rejection has no single line to name, and does not invent one.
THE OTHER HALF
Native guardrails protect what a model is asked and what it answers. They do not govern an agent writing to a system of record — and most SaaS platforms expose no guardrail format to compile into at all. Those are governed at the action boundary instead.
The two are complementary rather than alternatives. A guardrail compiled into Bedrock constrains the model interaction; the action boundary decides whether the resulting tool call is allowed to change anything.
WHERE THIS SITS
Each cloud has its own page describing connection, discovery and which outcomes its enforcement point can execute. This is the layer above them.
STATED PRECISELY
The compiler produces the native configuration and the record that it was produced from a reviewed policy. Attaching that configuration to the provider automatically is not claimed here.
IN THE PRODUCT